
The digital infrastructure of the modern world is currently facing one of its most significant stress tests in recent memory. A critical, high-severity vulnerability discovered in PHP—the server-side scripting language that serves as the backbone for over 70% of the internet—has sent shockwaves through the global technology landscape. From the content management systems (CMS) powering small business blogs to the complex enterprise architecture of global shipping hubs and governmental portals, millions of websites are currently operating in the “blast zone.”
As security researchers and software developers scramble to deploy patches, the incident has highlighted the fragility of the web’s foundational layers. With reports of major organizations taking their digital assets offline to prevent exploitation, the industry is bracing for a sustained period of vulnerability.
The Anatomy of the Threat: What You Need to Know
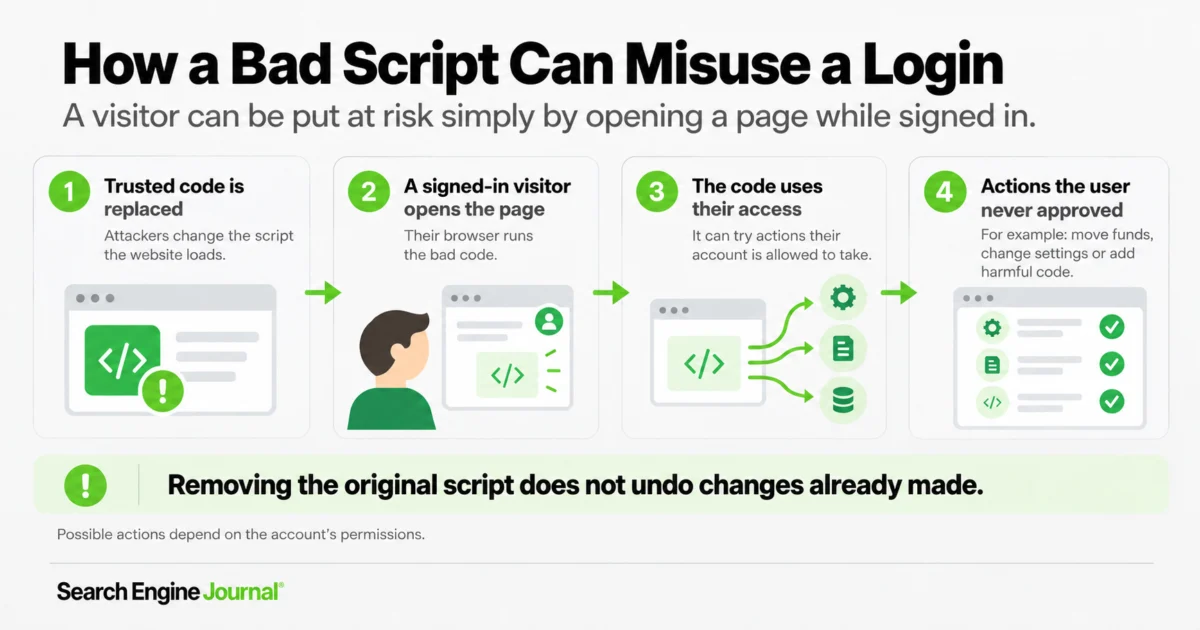
At its core, the vulnerability allows for Remote Code Execution (RCE). In the world of cybersecurity, an RCE is the “holy grail” for malicious actors. It permits an attacker to bypass authentication protocols and execute arbitrary code on a server without needing valid credentials. Effectively, if a server is running an unpatched version of PHP, an attacker could potentially gain full control of the web server, manipulate or steal sensitive databases, install ransomware, or use the compromised machine as a pivot point to launch further attacks on internal private networks.
Because PHP is the primary engine behind platforms like WordPress, Drupal, and countless custom-built business applications, the scope of this flaw is nearly unprecedented. The vulnerability does not discriminate based on industry; it threatens e-commerce sites holding credit card data, healthcare portals containing patient records, and government interfaces providing essential public services.
A Chronology of the Crisis
The unfolding of this security event has been rapid, characterized by a cascading series of warnings and reactive measures across the globe.
- October 21, 2026: The vulnerability is formally identified and verified. The organization behind PHP, along with security researchers, begins the urgent process of cataloging the exploit’s impact and developing remediation pathways.
- October 21–22, 2026: As technical details reach the public domain, threat intelligence agencies in the U.S. (CISA) and Australia (ASD) issue emergency alerts. The tone is unequivocal: "Patch immediately or risk total compromise."
- Mid-to-Late October 2026: Major infrastructure entities begin to weigh the risks. The Port of Rotterdam, acting out of an abundance of caution, announces the temporary suspension of certain web services. This signals a turning point where the vulnerability shifts from a technical issue to an operational crisis.
- Late October 2026: International bodies and national cybersecurity centers continue to monitor the situation. While official patches are released by the PHP development team, the “long tail” of the crisis begins—the arduous process of identifying, patching, and auditing millions of legacy sites that may not have active maintenance teams.
Supporting Data: Why PHP Remains the Primary Target
To understand the severity of this incident, one must understand the ubiquity of PHP. According to recent market analysis, despite the rise of modern alternatives like Node.js, Python, and Go, PHP remains the dominant server-side language.
- Market Share: With approximately 71% to 75% of the web relying on PHP, it is the undisputed language of the internet’s infrastructure.
- The CMS Factor: WordPress, which powers over 40% of all websites globally, is built entirely on PHP. This creates a monolithic attack surface; a single vulnerability in the core language can theoretically be weaponized against a massive portion of the world’s websites simultaneously.
- Legacy Debt: A significant percentage of these sites run on outdated versions of PHP. Many businesses have not updated their server environments in years, often due to the fear that a version update will “break” their custom code or legacy plugins. This "technical debt" has now become a major security liability.
Global Official Responses: A Unified Front
The international response to the PHP vulnerability has been coordinated and swift, reflecting the severity of the threat.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has been at the forefront, categorizing the flaw as a critical risk to national security. Their advisory notes that, “The exploitability of this vulnerability is high, and the potential for lateral movement within compromised networks makes immediate patching non-negotiable.”
Similarly, the Australian Signals Directorate (ASD) has issued guidance urging Australian businesses—particularly those in the e-commerce and logistics sectors—to perform an immediate audit of their web stacks. The ASD has emphasized that for organizations unable to patch immediately, the only safe recourse is to place the affected servers behind strict firewalls or take them offline entirely until the necessary updates are applied.
In Europe, the response has been characterized by proactive caution. European government agencies have gone as far as to warn that “websites may need to be taken offline” if they cannot guarantee the integrity of their server environments. This reflects a shift in the philosophy of incident response: in the past, organizations might have risked staying online while working on a fix; today, the risk of data exfiltration is deemed too high to justify uptime.
Implications for the Future of Web Security
This crisis serves as a stark reminder of the “Open Source Paradox.” While open-source projects like PHP empower millions of businesses and developers to build robust tools at little to no cost, they also create single points of failure. When the foundation cracks, the entire house shakes.
1. The Death of "Set and Forget"
For years, many small businesses have treated their websites as “set and forget” assets. This incident proves that in 2026, a website is a living, breathing software project that requires constant maintenance. The era of neglecting server-side updates is effectively over.
2. Mandatory Security Audits
Companies can no longer afford to rely on black-box hosting solutions without understanding what is running underneath. CTOs and business owners must now prioritize deep-stack audits. Understanding the version of PHP, the dependencies, and the server configuration is now a baseline requirement for risk management.
3. The Shift Toward Decentralized Architecture
While PHP remains dominant, this event may accelerate the transition toward more modern, containerized, or microservices-based architectures where dependencies are isolated. If a single point of failure can threaten 70% of the web, the industry will inevitably move toward a more fragmented and resilient landscape.
4. Supply Chain Vigilance
This vulnerability highlights the need for a more rigorous software supply chain. Developers must move toward "Secure by Design" principles, where automated patching and real-time monitoring are baked into the deployment pipeline rather than treated as an afterthought.
What Businesses Should Do Right Now
For organizations, startups, and developers still navigating the aftermath, the directive is clear:
- Inventory Your Assets: Identify every server and application that utilizes PHP. This includes not just your primary website, but also staging environments, internal tools, and legacy portals.
- Patch Immediately: Ensure all servers are updated to the latest, secure versions of PHP provided by the official PHP development team.
- Audit Your Stack: Use this as an opportunity to review your security posture. Are you using deprecated plugins? Are your server permissions set correctly? Is your database access restricted to only what is necessary?
- Communicate: If you are a service provider, keep your clients informed. Transparency is key to maintaining trust during a security crisis.
- Plan for the Worst: If your system is mission-critical and cannot be patched immediately, have an incident response plan ready to take the system offline to protect user data.
Conclusion
The 2026 PHP vulnerability is a watershed moment for the digital economy. It has exposed the deep-seated interdependencies of our global web infrastructure and reminded us that the convenience of the internet comes with a hidden cost of constant vigilance. While the internet will undoubtedly recover, the way businesses approach their digital architecture will be irrevocably changed. Security is no longer a feature—it is the foundation. As we move forward, the question for developers and business leaders alike will not be whether they can build faster, but whether they can build more securely.
